IBM on assignment at Toyota
Overview
Toyota Motor North America's supply chain products needed a modernized Role Management tool to be part of their internal platform.
This tool needed to simplify access control, enhance security and improve efficiency in requesting access. Job responsibilities and access permissions need to be clearly defined and organized to maintain order and security.
My Role: Product Designer
My Team: 1 CPO, 1 Tech PO, 1 design director, 5 developers
I Owned: User stories, wireframes, systems thinking, prototyping, user interviews
I Collaborated: Information architecture, design system components design reviews
Timeline: Oct 2024 – Mar 2026
Requesting Access (All cube users)
I worked closely with my Tech PO who was leading the modernization. We started with quickly creating user stories focusing on Cube Users requesting access and Notification Admins approving those requests.


My Tech PO also walked me through the legacy tool being used for Cube product access control. He highlighted the following painpoints multiple different Cube users have emphasized to him.
Legacy PAIN POINTS
Only authorized users can request access for unauthorized users
Too many disorienting actions in the landing page
Users can only request for roles, unclear what features are being requested for within those roles.
Separate process from the Cube platform.


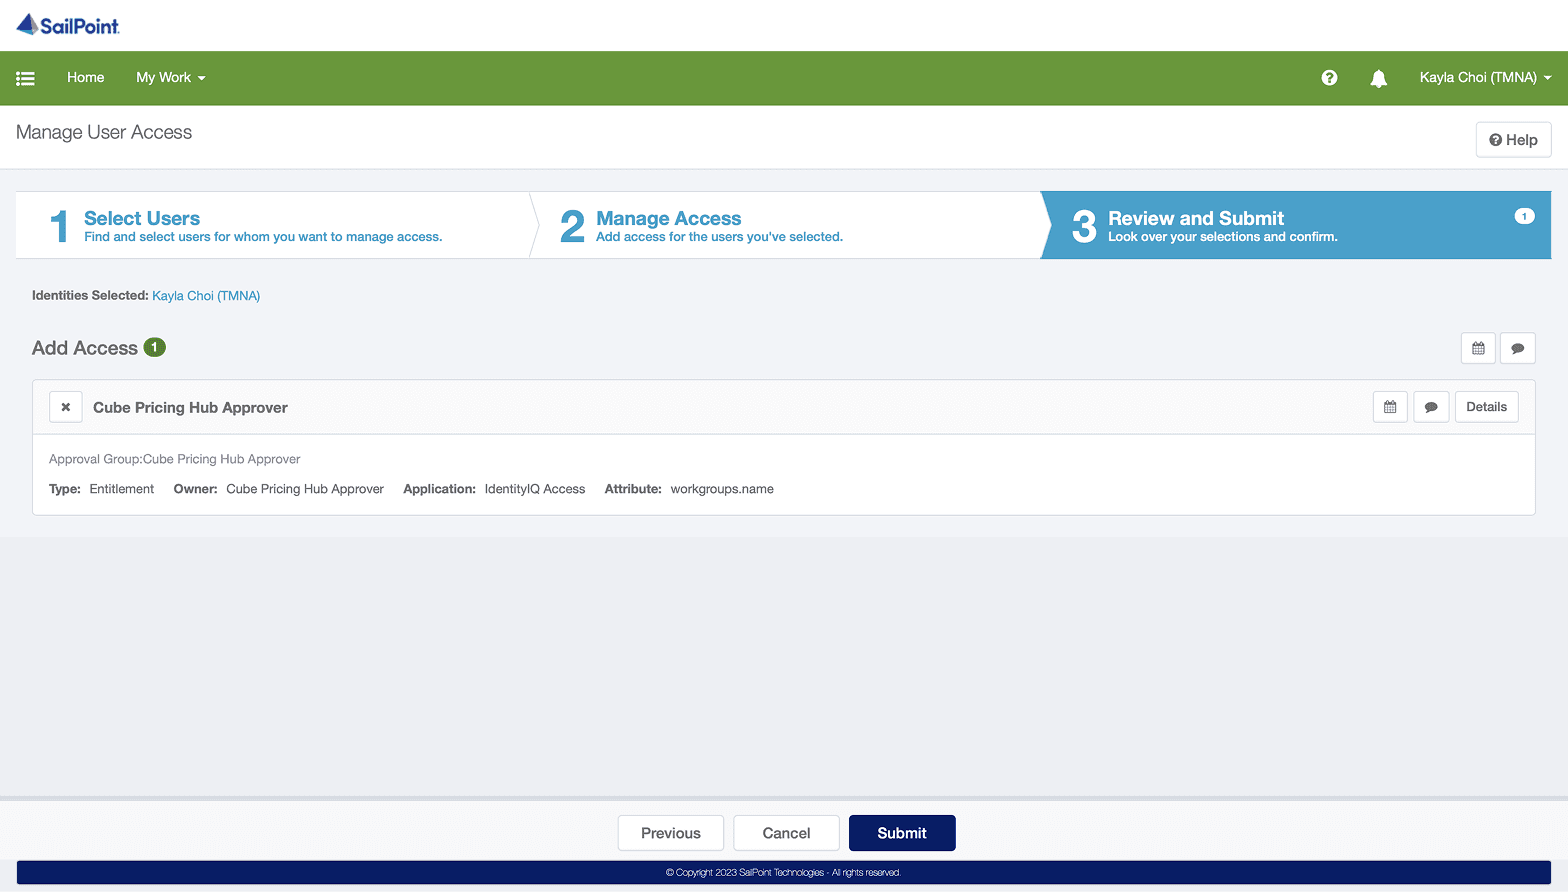

The first high-fidelity design was very simple using dropdowns to select Roles. How ever after receiving feedback from users we realize we needed a more granular and visually organized approach.
Instead of users selected Roles they now instead select the features within those Roles. We switched over to using cards to organize those features that users are able to search through, filter and collapse.


Approving Access Requests (Admins)
Enables admins to easily see all requests that needs actioning from them. They're able to click into request for more details or do a bulk action across requests if needed.


User access visibility and management (Admins)
Supports admins in managing user access. Gives them visibility into user roles, requests, departments and regions.


Creation and Management of Roles and Features (Admins)
Supports admins in managing what users are able to request access to. Product owners can also edit this as their features evolve and grow.

Requesting Access (Users)
Allows any users to request access from Cube. They're able to select specific features and permissions of what they need access to rather than all-or-nothing role access.
I also designed a logo that built upon the client’s existing brand, aligned to Role Management’s purpose, and amplifies its visibility.
This logo design centers a profile icon surrounded by a larger cube, to symbolize users encased in their role.
The yellow-gold color conveys high value, emphasizing how essential role management is to the seamless operation of every product in Cube.

Built a system engineered to scale and manage systemic permissions for Toyota's 10,000+ Supply Chain employees.
Accelerated access requests pending time by 30% for end users.
Designed business needs in an iterative agile approach.
Worked closely with engineering teams to anticipate anomalies and reduced costly rework by 20%.
Through designing this product I learned user testing is essential as our assumptions were not always true. Our first version failed because we assumed users wanted a simple design with the same organization they were using in the legacy tool. However, after user interviews I learned they'd rather have more flexibility and control in selecting features instead of ambiguous roles. They also wanted actions clear and consistent, either labeled as an action or as a button with the same actionable blue pattern used through the rest of the Cube platform.